IIS 8 and IIS 8.5 SSL Certificate CSR Creation
If you already have your SSL Certificate and just need to install it, see IIS 8 and IIS 8.5 SSL Certificate Installation.
How to create a CSR on Windows Server 2012 - IIS 8 and Windows Server 2012 R2 - IIS 8.5
You can use the to create your CSR and to automatically install the certificate on any Windows server.
- From the Start screen, click or search for Internet Information Services (IIS) Manager and open it.
- Click on the server name.
- From the center menu, double-click the "Server Certificates" button in the "IIS" section (it is in the middle of the menu).

- Next, from the "Actions" menu (on the right), click on "Create Certificate Request..." This will open the Request Certificate wizard.

- In the "Distinguished Name Properties" window, enter the information as follows:
Common Name - The name through which the certificate will be accessed (usually the fully-qualified domain name, e.g., www.domain.com or mail.domain.com).
Organization - The legally registered name of your organization/company.
Organizational unit - The name of your department within the organization (frequently this entry will be listed as "IT," "Web Security," or is simply left blank).
City/locality - The city in which your organization is located.
State/province - The state in which your organization is located.
Country/region - If needed, you can find your two-digit country code in our list.

- Click Next.
- In the "Cryptographic Service Provider Properties" window, enter the following information and then, click Next:
Cryptographic service provider - In the drop-down list, select Microsoft RSA SChannel..., unless you have a specific cryptographic provider.
Bit length - In the drop-down list, select 2048 (or higher).

- Click the ... box to browse to a location where you want to save the CSR file. If you just enter a filename without browsing to a location, your CSR will end up in C:\Windows\System32.
Remember the filename that you choose and the location to which you save it. You will need to open this file as a text file and copy the entire body of it (including the Begin and End Certificate Request tags) into the online order process when prompted.

- After you receive your SSL Certificate, you can install it.
After DigiCert issues your SSL Certificate, you will first need to install it to the server from which the certificate request was generated. Instructions for:
How to install and configure your SSL Certificate on Windows Server 2012 - IIS 8 and Windows Server 2012 R2 – IIS 8.5 (Single Certificate)
- Open the ZIP file containing your certificate. Save the file named your_domain_name.cer to the desktop of the web server you are securing.
- From the Start screen, click or search for Internet Information Services (IIS) Manager and open it.
- Click on the server name.
- From the center menu, double-click the "Server Certificates" button in the "IIS" section (it is in the middle of the menu).
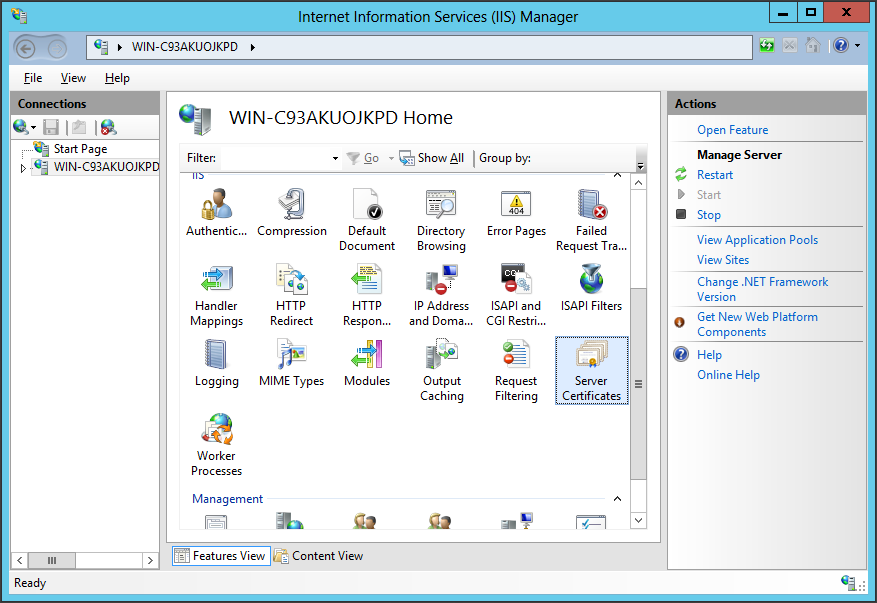
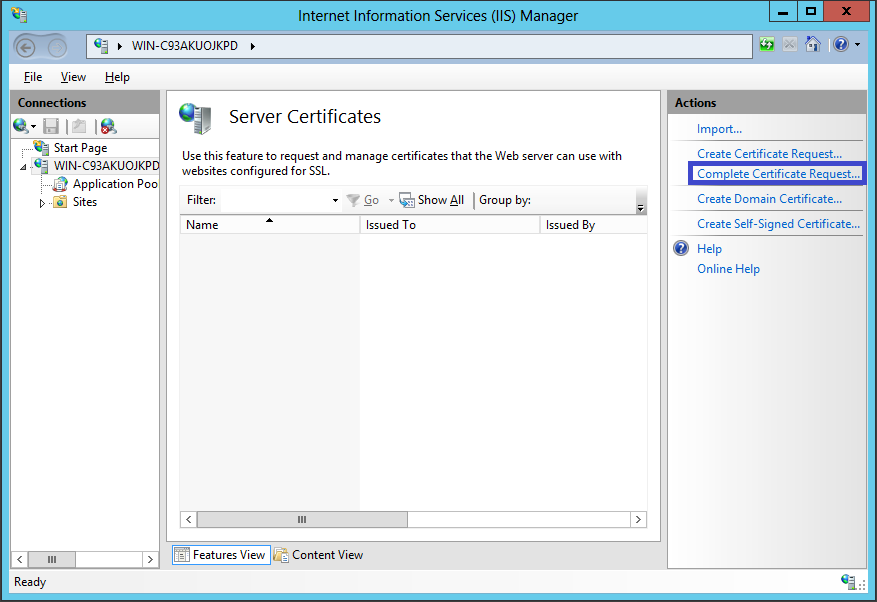
- From the "Actions" menu (on the right), click on "Complete Certificate Request..." This will open the Complete Certificate Request wizard.
- Browse to your_domain_name.cer file that was provided to you by DigiCert. You will then be required to enter a friendly name. The friendly name is not part of the certificate itself, but is used by the server administrator to easily distinguish the certificate. Choose to place the new certificate in thePersonal certificate store.
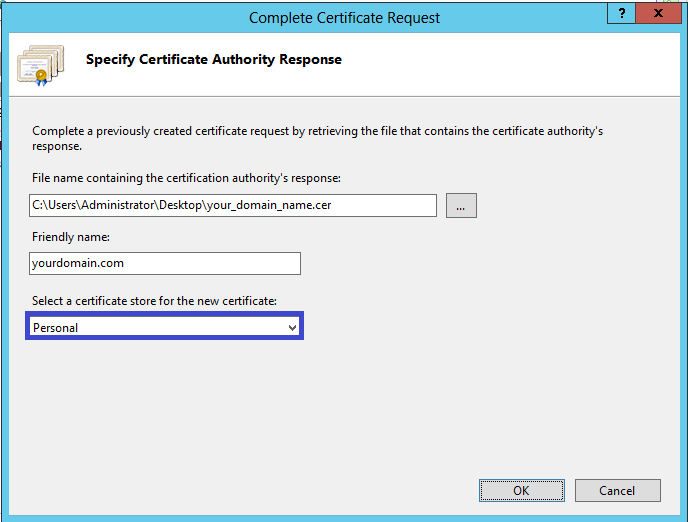
- Clicking "OK" will install the certificate to the server.
- Once the SSL Certificate has been successfully installed to the server, you will need to assign that certificate to the appropriate website using IIS.
- From the "Connections" menu in the main Internet Information Services (IIS) Manager window, select the name of the server to which the certificate was installed.
- Under "Sites," select the site to be secured with SSL.
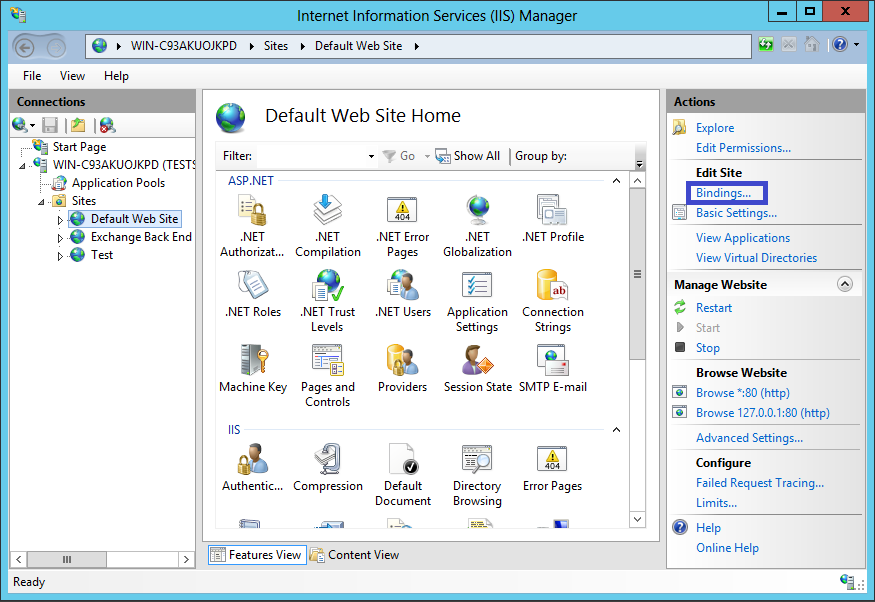
- From the "Actions" menu (on the right), click on "Bindings..." This will open the "Site Bindings" window.
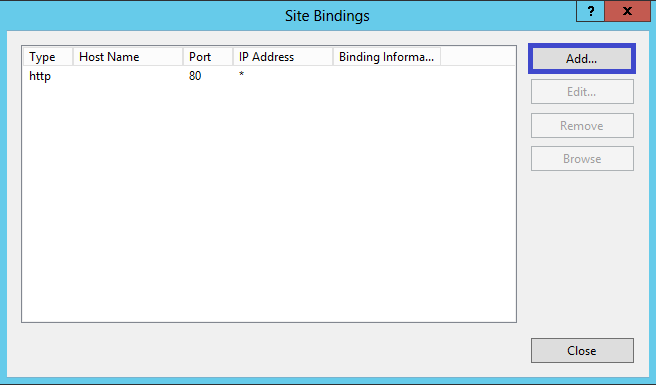
- In the "Site Bindings" window, click "Add..." This will open the "Add Site Binding" window.
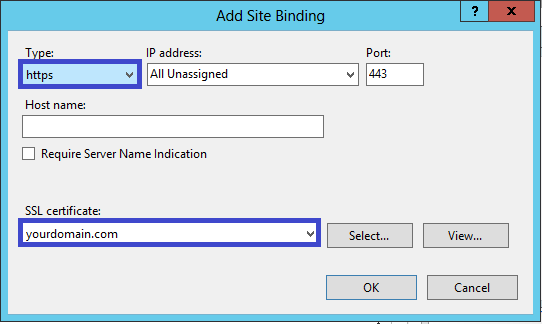
- Under "Type" choose https. The IP address should be the IP address of the site or All Unassigned, and the port over which traffic will be secured by SSL is usually 443. The "SSL Certificate" field should specify the certificate that was installed in step 7.
- Click "OK."
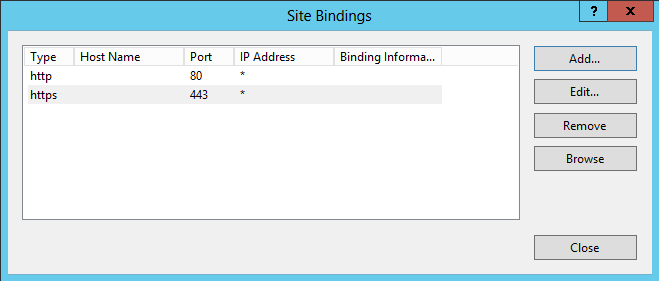
- Your SSL certificate is now installed, and the website configured to accept secure connections.
To enable your SSL certificate for use on other Windows servers, see our PFX export instructions for help.
How to install and configure your SSL Certificate on Windows Server 2012 - IIS 8 and Windows Server 2012 R2 - IIS 8.5 (Multiple Certificates Using SNI)
- Open the ZIP file containing your certificate. Save the file named your_domain_name.cer to the desktop of the web server you are securing.
- From the Start screen, click or search for Internet Information Services (IIS) Manager and open it.
- Click on the server name.
- From the center menu, double-click the "Server Certificates" button in the "IIS" section (it is in the middle of the menu).
- From the "Actions" menu (on the right), click on "Complete Certificate Request..." This will open the Complete Certificate Request wizard.
- Browse to your_domain_name.cer file that was provided to you by DigiCert. You will then be required to enter a friendly name. The friendly name is not part of the certificate itself, but is used by the server administrator to easily distinguish the certificate. Choose to place the new certificate in the Web Hosting certificate store.
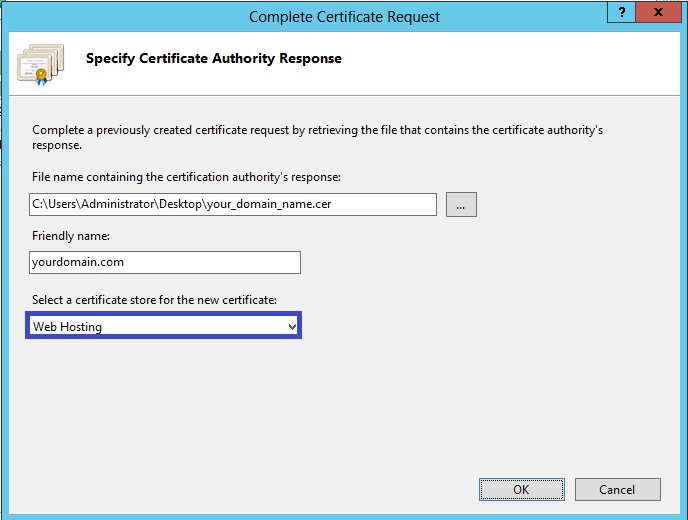
- Clicking "OK" will install the certificate to the server.
Note: There is a known issue in IIS 8 giving the following error: "Failed to remove the certificate" If this is the same server that you generated the CSR on then, in most cases, the certificate is actually installed. Simply cancel the dialog and press "F5" to refresh the list of server certificates. If the new certificate is now in the list, then it did install to the server, but you may want to check and make sure the certificate is in the Web Hosting certificate store. If not, you can move it there (see our How to Move Certificate to Another Certificate Store instructions) If it is not in the list, you will need to reissue your certificate using a new CSR (see our CSR creation instructions for IIS 8). After creating a new CSR, login to your DigiCert account and click the re-key button for your certificate. - Once the SSL Certificate has been successfully installed to the server, you will need to assign that certificate to the appropriate website using IIS.
- From the "Connections" menu in the main Internet Information Services (IIS) Manager window, select the name of the server to which the certificate was installed.
- Under "Sites," select the site to be secured with SSL.
- From the "Actions" menu (on the right), click on "Bindings..." This will open the "Site Bindings" window.
- In the "Site Bindings" window, click "Add..." This will open the "Add Site Binding" window.
- Under "Type" choose https. The IP address should be the IP address of the site or All Unassigned, and the port over which traffic will be secured by SSL is usually 443. The "SSL Certificate" field should specify the certificate that was installed in step 7.
- Click "OK."
- Your first SSL certificate is now installed, and the website configured to accept secure connections.
- Repeat the steps for creating a CSR for your 2nd+ site.
- Install the certificate file as mentioned above, up through step 12.
- Under "Type" choose https. The IP address should be the IP address of the site or All Unassigned, and the port over which traffic will be secured by SSL is usually 443. Enter the host name you will be securing and check the box that says Require Server Name Indication. This is required for all additionalsites (not required on the primary site as shown in step 13) The "SSL Certificate" field should specify the certificate that was installed in step 7 for your additional certificate.
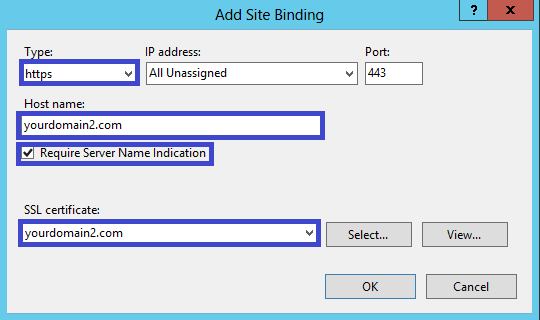
- Click "OK."
- Your second SSL certificate is now installed, and the website configured to accept secure connections.
- Repeat steps sixteen through nineteen to set up any other additional sites.