The last firmware update attempt was not successful. Ready for the next update.
Sonntag, 13. Oktober 2013
ILO update 1.16 to 1.55 fails - use 1.28 as intermediate version
Just tried to update ILO3 on a HP DL 380 G7 from version 1.16 (Dec 17 2010) to one of the latest version 1.55 (Feb 19 2013) but got the following error message in the browser:

Freitag, 11. Oktober 2013
UPGRADING VMWARE VCENTER APPLIANCE 5.X TO 5.5
Last week VMware vSphere 5.5 went GA, so it is time to update the home lab to the latest version. I am using the VMware vCenter Appliance (VCSA), and it is the latest version. I never did an upgrade of the VCSA so I start searching the knowledgebase of VMware and found an article describing the upgrade process (VMware KB2058441).
Prerequisites
Prerequisites
- Before attempting the upgrade, if you are using custom SSL certificates, ensure that they meet the requirements as per Configuring Certificate Authority (CA) signed certificates for vCenter Server Appliance 5.5 (2057223).
- Ensure that you have taken a backup/snapshot of your existing vCenter Server Appliance and the external database.
Procedure
- Deploy the new VMware vCenter Appliance.
- Connect to both the old and new appliances in separate browser windows. For example, use a URL similar tohttps://ip_address_of_vCenter_VM:5480
- In the new appliance, start the vCenter Server Setup wizard and accept the end user license agreement.
- In the Configure Options panel, select Upgrade from previous version and then click Next.
- Copy the key from the Import this key into the source appliance field.
- If you are upgrading vCenter Server Appliance 5.0.x to 5.5:
- In the old vCenter Server Appliance 5.0, click the Appliance Upgrade tab.
- Select source for the appliance role and click Set role.
- Click Establish Trust.
- Paste the local appliance key into the Remote appliance key field.
- Click Import remote key.
- Copy the local appliance key.
- In the new vCenter Server Appliance 5.5, paste the local appliance key into the Remote appliance key field and click Next.
- If you are upgrading vCenter Server Appliance 5.1 to 5.5:
- In the old vCenter Server Appliance 5.1, paste the key from Step 5 into the Upgrade key field.
- Click Import key.
- Stop vCenter Server.
- Copy the Upgrade key.
- In the new appliance, paste the Upgrade key to the Paste the source appliance key into the field below field and click Next.
- If there are issues detected with your SSL certificates, select the Replace the SSL certificates option. You are prompted for SSO password for user admi...@vsphere.local.
This looks pretty easy. First I deployed a new VCSA with a new name (VCSA 5.5), configured the IP settings, different than my original VCSA (VCSA 5.1). After the OVF deployment I started the VCSA and went to the management page. I accepted the EULA on my new VCSA 5.5.
Mittwoch, 9. Oktober 2013
How to Whitelist a domain or email in Exchange 2010
If you have the Edge Transport Role installed on an Exchange 2010, mail may be rejected with the following error:
My.User@domain.com
 mail.domain.com #<mail.domain.com #5.7.1 smtp; 550 5.7.1 Message rejected as spam by Content Filtering.> #SMTP#
it appears the only way to whitelist in Exchange 2010 is through the Powershell – not the GUI.
Specific Address
1
2
3
| $list = (Get-ContentFilterConfig).BypassedSenders$list.add("new.mail@address.com")Set-ContentFilterConfig -BypassedSenders $list |
Entire Domain
1
2
3
| $list = (Get-ContentFilterConfig).BypassedSenderDomains$list.add("domain.com")Set-ContentFilterConfig -BypassedSenderDomains $list |
Verify
1
| Get-ContentFilterConfig |
Dienstag, 3. September 2013
How To Enable SSL 3.0 Server 2008 /SBS 2008/SBS2011
Problem
Server 2008,server 2008 SBS and SBS 2011 do have the functionality for SSL 3.0 however by default it does not understand anything that tries to connect with this protocol. For security reasons if you need to enable SSL 3.0 on your server we can enable it with some additional registry keys. Follow the step by step guide below.
Resolution
(MAKE SURE THAT YOU BACKUP YOUR REGISTRY BEFORE APPLYING THOSE CHANGES)
• Using regedit to add the following keys ( right click on protocols -> new -> key -> “SSL 2.0″ then “SSL 3.0″ then “TLS 1.0″ )HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 2.0 HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 3.0 HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.0
• Under each of the keys above you need to create additional keys “Client” and “Server”
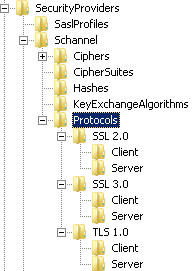
Enable ssl 3.0
For SSL 2.0:HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 2.0\Client HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 2.0\Server
For SSL 3.0:HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 3.0\Client HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\SSL 3.0\Server
For TLS 1.0:HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.0\Client HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Protocols\TLS 1.0\Server
Then you will have to create DWORD (32bit) value called “Enabled” under each “Client” and “Server” key for “SSL 2.0, SSL 3.0 and TLS 1.0″
DWORD (32bit) Value
Value name = Enabled
Value date = 0
Value date can be set to “1″ – Enabled or “0″ – Disabled
In my scenario the values were “enabled” (set to 1) for SSL 3.0 and TLS 1.0 and “disabled” (set to 0) for SSL 2.0
Here is a disabled value for ssl 2.0

Enable ssl 3.0 server 2008
and here is SSL 3.0 enabled

Enable ssl 3.0 server 2008
• Next step is to add correct Ciphers, to do so you will have to navigate to the following key in the registryHKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Ciphers
• (right click on “Cliphers” New -> Key)HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Ciphers\RC2 128/128 HKEY_LOCAL_MACHINESYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Ciphers\RC4 128/128 HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\ Control\SecurityProviders\SCHANNEL\Ciphers\Triple DES 168/168
• That’s all! Now you need to restart your server to apply those changes.
• If you are using TMG 2010 or ISA 2006 to publish the website externally you will need to apply exactly the same settings to registry to it.
Mittwoch, 24. Juli 2013
Manage an HP Smart Array directly from VMware ESXi
In my lab I’m using a Proliant DL380 G5 filled with disk as a storage server, running some VSA on top of the volume I created and formatted with a vmfs filesystem.

From here, let the fun begin! There are many commands you can run on the raid controller by running /opt/hp/hpacucli/bin/hpacucli, I’m going to show you some of them:

First, I identified the controller. Remember is in slot 3, this will be needed in the next commands.
As I said, my problem seemed to be related to the cache battery, so I went to check its status:

The status seems to be ok, but I went to enable anyway the cache, the command is:
1 | ctrl slot=3 modify dwc=enable forced |
Go to check it. As a last example, a fun stuff:

First, I identified the physical disks in the controller (pd), then I enabled the led on every single disk. This is the result
So you can see from the output above that there’s a 1.4Tb Logical Drive and 2 unassigned 300Gb SAS drives. I ran
=> ctrl slot=0 array A add drives=2I:1:7
which added disk 7 into the array. This process took just over 24 hours.
I then ran:
=> ctrl slot=0 array A add drives=2I:1:8
which added disk 8 into the array. This process also took just over 24 hours.
A further running of
=> ctrl slot=0 show config detail
showed that both drives were added to the array. However the space as reported in the HP System Manager was still 1.4Tb (same as before).
The last step was to expand the array:
=> ctrl slot=0 ld 1 modify size=max
Once this had completed (it took a couple of seconds), all that needed to happen was a reboot for Windows to recognise the new space. I then connected to the Hyper-V host via Computer Management and extended the available space with Disk Management.
*****Command Summary *****
Utility Keyword abbreviations
| |
| Abbreviations | chassisname = ch controller = ctrl logicaldrive = ld physicaldrive = pd drivewritecache = dwc |
hpacucli utility
| |
| hpacucli | # /opt/hp/hpacucli/bin/hpacucli (start ACUCLI --ESX HSOT) # hpacucli # hpacucli help Note: you can use the hpacucli command in a script |
Controller Commands
| |
| Display (detailed) | hpacucli> ctrl all show config hpacucli> ctrl all show config detail |
| Status | hpacucli> ctrl all show status |
| Cache | hpacucli> ctrl slot=0 modify dwc=disable hpacucli> ctrl slot=0 modify dwc=enable |
| Rescan | hpacucli> rescan Note: detects newly added devices since the last rescan |
Physical Drive Commands
| |
| Display (detailed) | hpacucli> ctrl slot=0 pd all show hpacucli> ctrl slot=0 pd 2:3 show detail Note: you can obtain the slot number by displaying the controller configuration (see above) |
| Status | hpacucli> ctrl slot=0 pd all show status hpacucli> ctrl slot=0 pd 2:3 show status |
| Erase | hpacucli> ctrl slot=0 pd 2:3 modify erase |
| Blink disk LED | hpacucli> ctrl slot=0 pd 2:3 modify led=on hpacucli> ctrl slot=0 pd 2:3 modify led=off |
Logical Drive Commands
| |
| Display (detailed) | hpacucli> ctrl slot=0 ld all show [detail] hpacucli> ctrl slot=0 ld 4 show [detail] |
| Status | hpacucli> ctrl slot=0 ld all show status hpacucli> ctrl slot=0 ld 4 show status |
| Blink disk LED | hpacucli> ctrl slot=0 ld 4 modify led=on hpacucli> ctrl slot=0 ld 4 modify led=off |
| re-enabling failed drive | hpacucli> ctrl slot=0 ld 4 modify reenable forced |
| Create | # logical drive - one disk hpacucli> ctrl slot=0 create type=ld drives=1:12 raid=0 # logical drive - mirrored hpacucli> ctrl slot=0 create type=ld drives=1:13,1:14 size=300 raid=1 # logical drive - raid 5 hpacucli> ctrl slot=0 create type=ld drives=1:13,1:14,1:15,1:16,1:17 raid=5 Note: drives - specific drives, all drives or unassigned drives size - size of the logical drive in MB raid - type of raid 0, 1 , 1+0 and 5 |
| Remove | hpacucli> ctrl slot=0 ld 4 delete |
| Expanding | hpacucli> ctrl slot=0 ld 4 add drives=2:3 |
| Extending | hpacucli> ctrl slot=0 ld 4 modify size=500 forced |
| Spare | hpacucli> ctrl slot=0 array all add spares=1:5,1:7 |
PXE boost SCCM 2012
PXE booting during a OS Deployment with ConfigMgr 2012 can be a bit slow on a Windows 2008 R2 / 2012 server. This is because Microsoft has set values that will suite most network environments.
But I want SPEED. Now what?
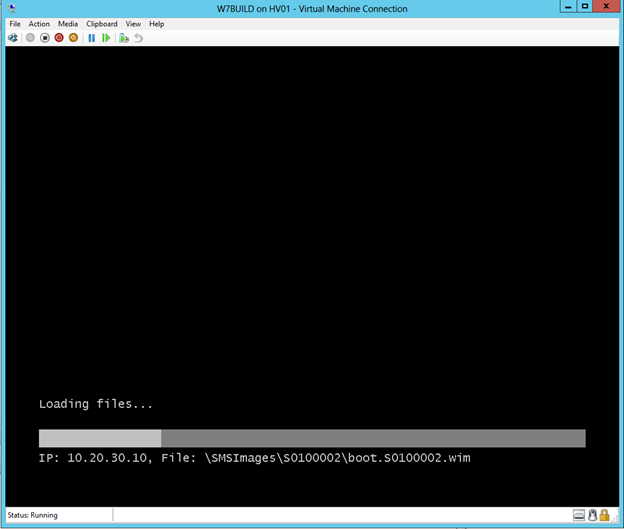
Good news. You can tweak your PXE-enabled Distribution Point!
Add a registry key:
HLKM\SOFTWARE\Microsoft\SMS\DP\RamDiskTFTPBlockSize
With a REG_DWORD value of MAX 4000 Hex!!
Then restart the WDS Service.
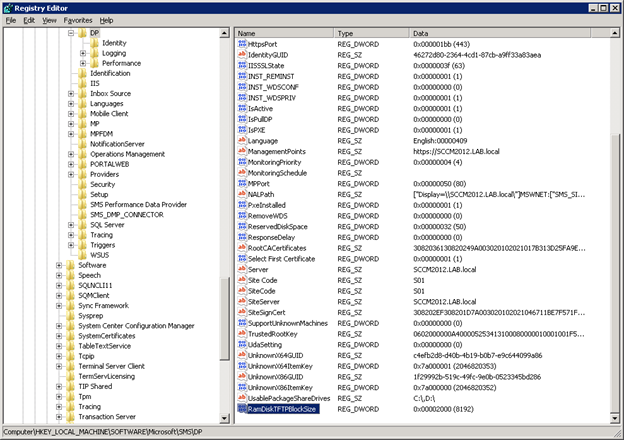
I set this value to 2000 Hex and speed is blazing fast!
Remember the higher value the more risk of packet loss if you have a bad network connection.
Try this out carefully in your network environment.
If you experience problems, lower the value.
Try this out carefully in your network environment.
If you experience problems, lower the value.
Donnerstag, 30. Mai 2013
Schwerwiegender Fehler bei der Systemvorbereitung des Computers - Sysprep
Ich wollte mir eben einen Referenzcomputer erstellen und habe als Administrator die Eingabeaufforderung geöffnet. Dann habe ich den Befehl
sysprep.exe /oobe /generalize /shutdowneingegeben. Zuerst schien die Sache auch zu laufen, doch plötzlich bekam ich die Fehlermeldung
Schwerwiegender Fehler bei der Systemvorbereitung des Computers.Seither geht bezüglich sysprep gar nichts mehr. Ich habe dann den Rechner neu gestartet und musste erstmal warten, weil scheinbar die ganzen Treiber schon rausgeworfen worden sind. Windows 7 hat sich dann die Treiber selbst wieder installiert, Neustart alles soweit wieder gut. Habe es dann erneut probiert, aber jetzt bekomme ich direkt nach dem Bestätigen des Befehls die Fehlermeldung.
Lösung:
MS hat eine KB dazu veröffentlicht: http://support.microsoft.com/kb/929828 MS bietet auch eine Anleitung als Lösung an
sysprep.exe /audit /generalize /shutdown /quiet /unattend:C:\unattend.xml
Unattend.xml:
<settings pass="generalize">
        <component name="Microsoft-Windows-Security-SPP" processorArchitecture="amd64" publicKeyToken="31bf3856ad364e35" language="neutral" versionScope="nonSxS" xmlns:wcm="http://schemas.microsoft.com/WMIConfig/2002/State" xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance">
            <SkipRearm>1</SkipRearm>
        </component>
</settings>
Donnerstag, 18. April 2013
Failed to connect to VMware lookup service
have been re-building my lab yesterday with all the latest vCloud suite 5.1 GA bits.
After deploying and configuring the vCenter Virtual Appliance, when I was trying to login to the vSphere web client, I kept receiving the error “ Failed to connect to VMware Lookup Service https://[hostname]:7444/lookupservice/sdk – SSL certificate verification failed. ” and could not login.

This issue occurs if you have changed the hostname or IP address of the vCenter Virtual Appliance. The certificate that was created on initial configuration is no longer valid. To resolve this issue, follow the steps below:
- Login into vCenter VA Configuration https://[hostname]:5480
- Select the Admin tab
- Click Toggle certificate setting, you will see Certificate regeneration enabled change to Yes.

- Re-boot the Virtual Appliance

During the bootup procedure you will see
Hostname or IP has changed. Regenerating self signed certificate.
Montag, 25. Februar 2013
PST Capture 2.0
Earlier this week, we released a brand new version of the free PST Capture tool that allows you to hunt down PST files on client computers across your network. After it finds PST files on users’ computers, the tool consolidates the PST files to a central location, and then easily injects PST data to primary or archive mailboxes on your on-premises Exchange Servers or Exchange Online.
What’s new in PST Capture 2.0?
PST Capture
2.0 includes the following improvements:- Support for Microsoft Exchange Server 2013
- Updated profile generation code to use Outlook Anywhere
(RPC over HTTP).
- Fixed Exchange Online import failure issue when PST
Capture is not installed on an Exchange server.
- Removed User Interface limit of 1,000 users when
performing an import to Exchange Online.
- General
performance improvements
Forefront Unified Access Gateway 2010 SP3
Ab sofort steht das Service Pack 3 für das Forefront UAG 2010 als kostenloser Download zur Verfügung. Die Änderungen sind im KB Artikel 2744025 dokumentiert. Zu den wichtigsten Neuerungen gehören
- Windows
8 Client Unterstützung (Mail App und Remote Desktop)
- Internet
Explorer 10 Browser Unterstützung
- Windows
Phone 8 Client Unterstützung
- Office
2013 Client Apps Unterstützung
- Remote
Desktop Client 8 (RDP8 Update für Windows 7 SP1)
- Exchange
2013 Application Publishing
- SharePoint
2012 Application Publishing
Donnerstag, 7. Februar 2013
vSphere client: Error 1406. Could not write value Productlanguage to key …
Got this nice notification trying to install the vSphere Client 4.1 on Server 2008 R2.
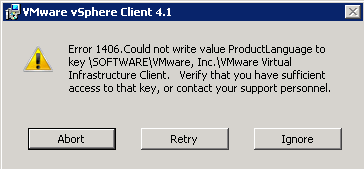
To fix this, you have to delete the following Registry key:
HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\VMware, Inc.
And press retry. The Sphere Client 4.1 setup will finish without errors.
Abonnieren
Posts (Atom)
-
One of the visitors of this blog asked the question if we could publish a list of recommended post Windows Server 2008 R2 SP1 hotfixes rela...
-
With your Windows Network working and a number of resources shared, you can install the TCP/IP Protocol to allow your Windows for Workgrou...
